
User Management Overview
The User Management screen is where you manage Users and Roles in your organization.
In Spirion Sensitive Data Platform (SDP), the User Management page (accessible via Settings > User Management) serves as the central administrative and governance control plane for identity, authentication, and platform access.
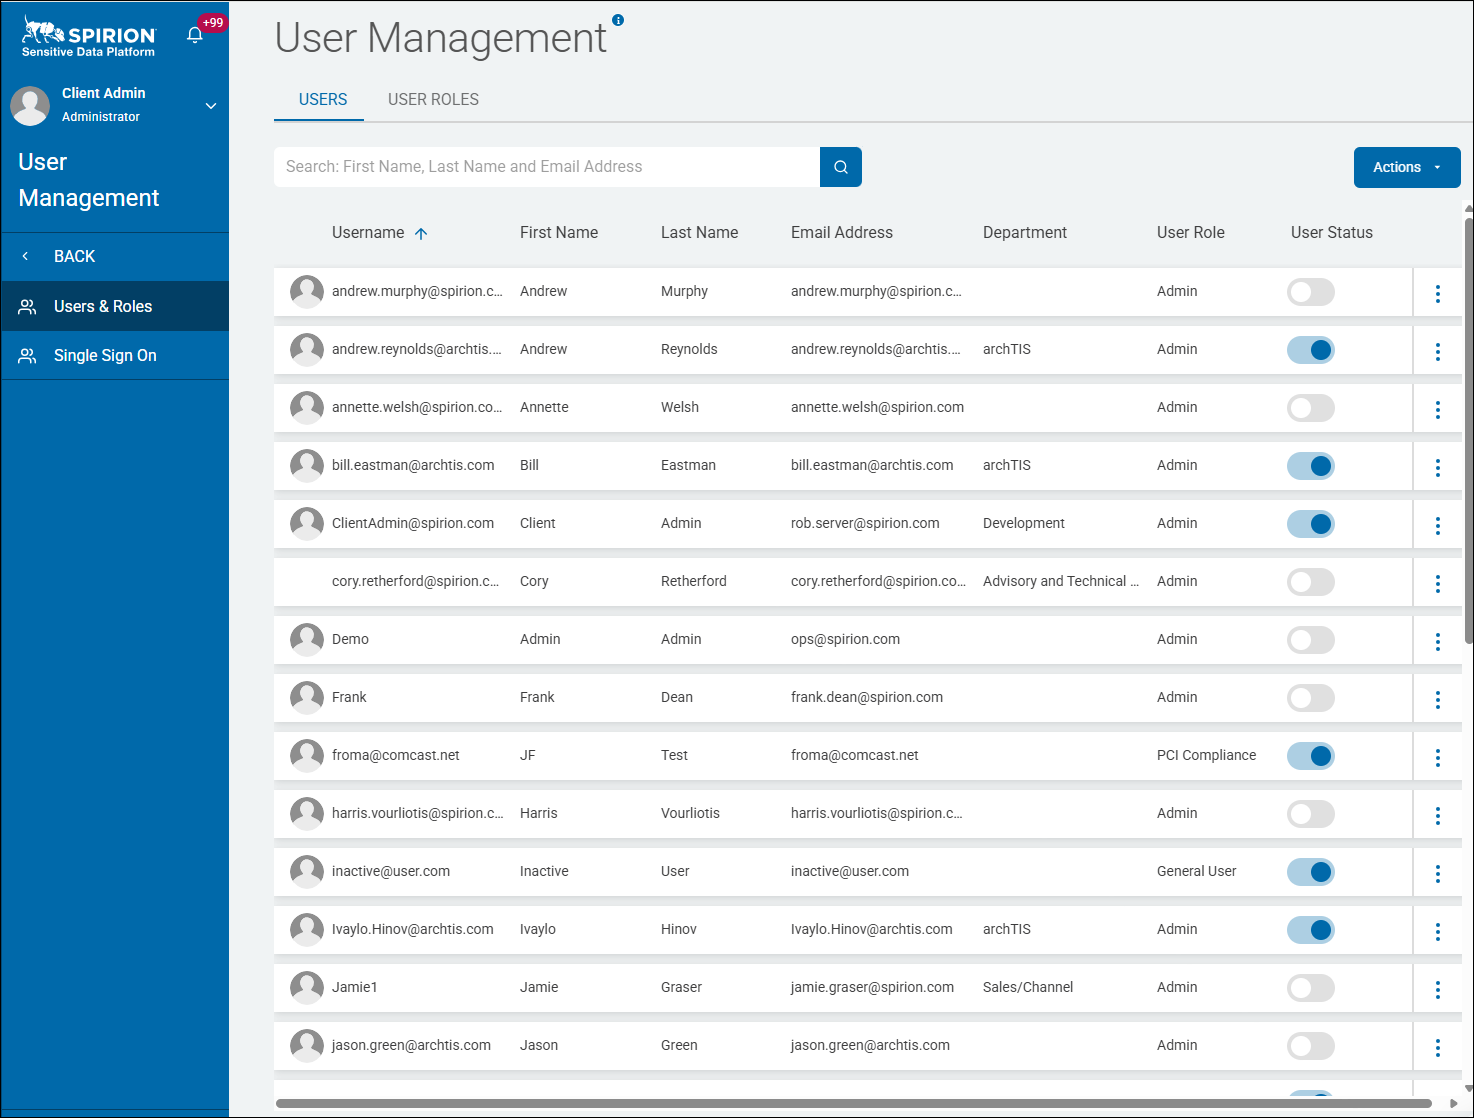
Important Functions Performed on the User Management Page
1. User Account Lifecycle Management (CRUD)
- Create Users: Provision new internal console users with essential identity fields (First Name, Last Name, Username, Email Address, and Role assignment) with email uniqueness validation.
- Edit & Maintain Users: Update contact details, modify role assignments, reset user credentials, or deactivate accounts as personnel change.
- Bulk Management: Onboard, update, or deactivate users at scale using CSV import capabilities or REST APIs.
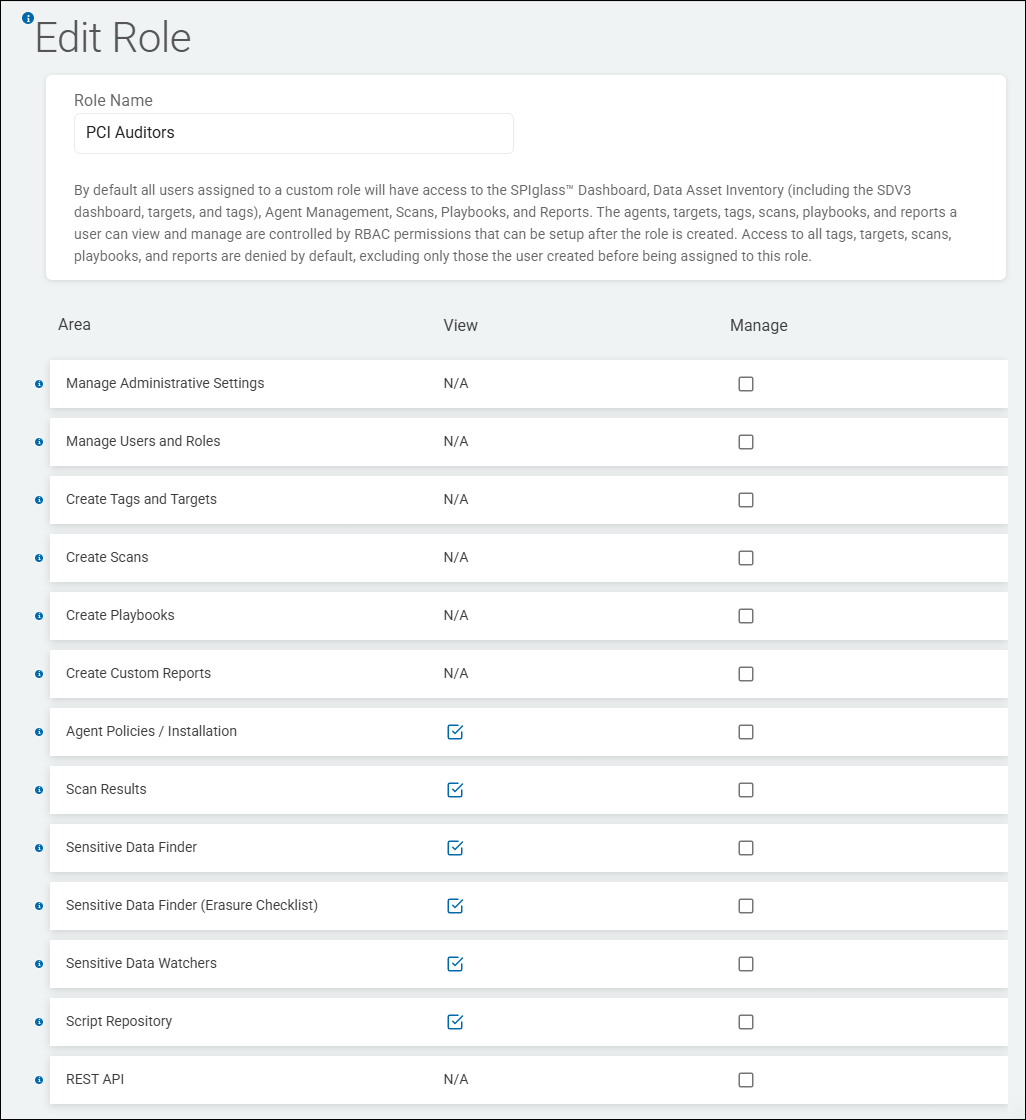
2. Role Creation and Customization
- Custom Role Definition: Create new organizational roles by providing a unique Role Name derived from predefined Base Roles.
- Role Activation / Deactivation: Toggle roles active or inactive based on evolving security policies without having to delete historical role audit trails.
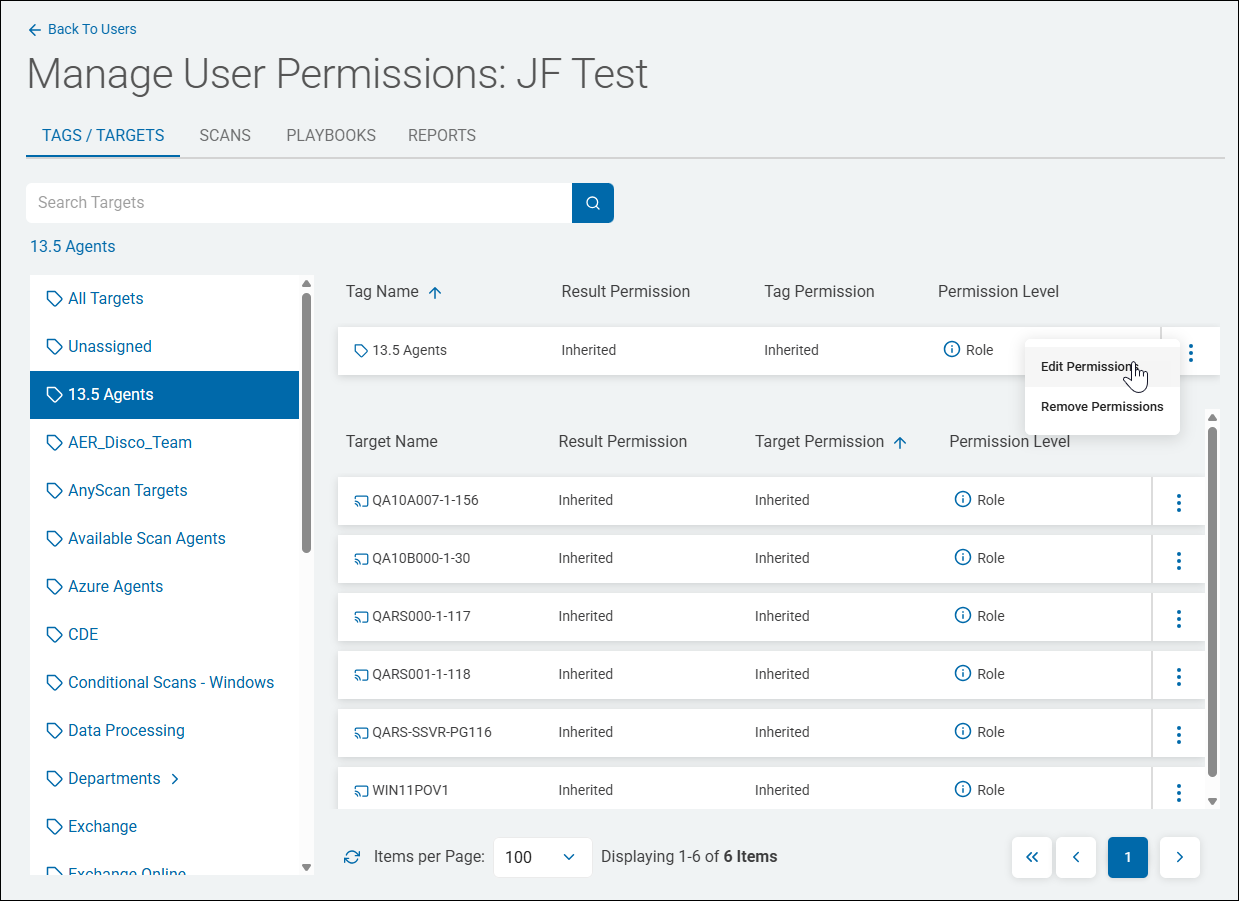
3. Role-Based Access Control (RBAC)
- Granularly define what platform modules and administrative capabilities a given role can view, edit, or execute across the console.
How User Management Relates to Other Functions in Spirion Sensitive Data Platform
User Management acts as the foundational access gatekeeper that determines who can interact with every other pillar of Spirion Sensitive Data Platform:
                      ┌────────────────────────┐
                      │    USER MANAGEMENT     │
                      │  (Identities & Roles)  │
                      └───────────┬────────────┘
                                  │
         ┌────────────────────────┼────────────────────────┐
         ▼                        ▼                        ▼
┌──────────────────┐    ┌──────────────────┐    ┌──────────────────┐
│ Scan & Policy    │    │ Results &        │    │ Analytics &      │
│ Operations       │    │ Remediation      │    │ Data Governance  │
└──────────────────┘    └──────────────────┘    └──────────────────┘
- Relation to Scans, Targets & Policy Configuration
- Creating and editing scan targets (endpoints, cloud storage, databases, SharePoint), defining scan scopes, or modifying discovery playbooks requires administrative privileges.
- User Management ensures that general operators cannot alter scan schedules, target credentials, or policy sensitivity rules.
- Relation to Results & Remediation Workflows
- Scan findings contain sensitive data locations, metadata, and match context.
- User Management controls who has permission to view search results, inspect match snippets, approve ignore rules, or trigger manual remediation actions
- For example, quarantine, redact, shred, etc.
- Relation to Reporting & the Data Warehouse
- Executive reporting, compliance dashboards (PCI DSS, HIPAA, GDPR), and data warehouse export queries expose organizational risk posture.
- User roles restrict reporting access so managers see aggregated trends and compliance statuses without exposing sensitive details to unauthorized staff.
- Relation to System Settings & Fleet Management
- Global settings—such as Agent registration tokens, environment integrations, notification endpoints, and tenant configurations—are restricted to high-tier roles defined and assigned within User Management.
You can: